説明
Headers Security Advanced & HSTS WP は最高のオールインワンで、すべての WordPress ユーザー向けの無料プラグインです。このプラグインを無効にすると、サイトの構成が以前の状態に正確に戻ります。
Headers Security Advanced & HSTS WP プロジェクトは、サイトが Web サイトのセキュリティを強化するために使用できる HTTP 応答ヘッダーを実装します。プラグインはすべてのベストプラクティスを自動的に設定します (何も考える必要はありません) 。これらの HTTP 応答ヘッダーは、最新のブラウザーが簡単に予測可能な脆弱性に遭遇するのを防ぐことができます。Headers Security Advanced & HSTS WP プロジェクトは、すべてのワードプレスユーザーにこれらのヘッダーの普及と認知度と使用率を高めたいと考えています。
このプラグインは OpenHeaders by irn3 によって開発されており、WordPress のセキュリティとベストプラクティスを重視しています。
Headers Security Advanced & の優れた機能を確認してください。 HSTS WP :
- X-XSS-Protection (非推奨)
- Pragma (非推奨)
- Public-Key-Pins (非推奨)
- Expect-CT (非推奨)
- Access-Control-Allow-Origin
- Access-Control-Allow-Methods
- Access-Control-Allow-Headers
- X-Content-Security-Policy
- X-Content-Type-Options
- X-Frame-Options
- X-Permitted-Cross-Domain-Policies
- X-Powered-By
- Content-Security-Policy
- Referrer-Policy
- HTTP Strict Transport Security / HSTS
- Content-Security-Policy
- Content-Security-Policy-Report-Only
- Clear-Site-Data
- Cross-Origin-Embedder-Policy-Report-Only
- Cross-Origin-Opener-Policy-Report-Only
- Cross-Origin-Embedder-Policy
- Cross-Origin-Opener-Policy
- Cross-Origin-Resource-Policy
- Permissions-Policy
- Strict-dynamic
- Strict-Transport-Security
- FLoC (コホートの複合学習)
Headers Security Advanced & HSTS WP は OWASP CSRF に基づき、ワードプレスサイトを保護します。OWASP CSRF を使用し、プラグインがインストールされると、出力で nonce を使用するメソッドを呼び出すことなく、CSRF を完全に軽減できます。 他の脆弱なプラグイン (CSRF) があっても、サイトは安全になります。
HTTP セキュリティヘッダーは、Web サイトのセキュリティの重要な部分です。Headers Security Advanced & で自動実装後、 HSTS WP は、サイトが遭遇する可能性のある最も悪名高い種類の攻撃からユーザーを保護します。これらのヘッダーは、XSS、コード インジェクション、クリックジャッキングなどから保護します。
コンテンツセキュリティポリシー(CSP) で主要なサービスを問題なく動作させるために多くの労力を注いでいます。以下は、Headers Security Advanced & HSTS WP でテスト・使用した例の一部です:
- Google Tag Manager 向けの CSP 使用
世界で最も人気のタグマネージャー - Gravatar 向けの CSP 使用
WordPress やソーシャルサイト向けのアバターサービス - WordPress Internal Media 向けの CSP 使用
WordPress のメディアをサポート - Youtube Embedded Video SDK 向けの CSP 使用
YouTube の埋め込みフレームと JS SDK をサポート - CookieLaw の CSP 使用
規制要件に対応するプライバシー技術 - Mailchimp の CSP 使用
Mailchimp のオートメーション、SDK、モジュールをサポート - Google Analytics の CSP 使用
stats.g.doubleclick.net や www.google.com などの基本的なコンバージョンドメインをサポート - Google Fonts の CSP 使用
ページ上で読み込んでいなくても、いずれかの SDK が使用している可能性が高い - Facebook 向けの CSP 使用
Facebook SDK の機能をサポート - Stripe 向けの CSP 使用
高いセキュリティを備えたオンライン決済システム - New Relic 向けの CSP 使用
登録・監視のためのユーティリティ - Linkedin Tags + SDKs 向けの CSP 使用
Linkedin Insight、Linkedin Ads、SDK をサポート - OneTrust 向けの CSP 使用
OneTrust のサポートにより、企業のプライバシー要件管理を支援 - Moat の CSP 使用
広告検証、ブランドセーフティ、広告、カバレッジなどの測定スイートを Moat がサポート - jQuery の CSP 使用
JS ライブラリである jQuery をサポート - Twitter Widgets & SDKs の CSP 使用
Connect、Widgets、Twitter のクライアントサイド SDK をサポート - Google Maps 向けの CSP 使用
ストリートビューで使用される ggpht を含む Google Maps をサポート - Quantcast Choice 向けの CSP 使用
GDPR や CCPA などのプライバシーに対応する Quantcast をサポート - Twitter Ads & Analytics の CSP 使用
広告と分析のための Twitter をサポート - Paypal 向けの CSP 使用
オンライン決済システムのための PayPal をサポート - Drift 向けの CSP 使用
Drift および Driftt をサポート - Cookiebot の CSP 使用
Cookie とトラッカーをサポートし、GDPR/ePrivacy および CCPA に準拠 - Vimeo Embedded Videos SDK の CSP 使用
フレーム、JS SDK、Froogaloop 連携をサポート - AppNexus (now Xandr) 向けの CSP 使用
カスタムリターゲティングのための AppNexus をサポート - Mixpanel 向けの CSP 使用
クライアントサイドのデータを収集する SDK/JS 対応の分析ツールをサポート - Font Awesome 向けの CSP 使用
CSS と Less によるフォントとアイコンのツールキットをサポート - Google reCAPTCHA 向けの CSP 使用
不正防止とボット対策のための reCAPTCHA をサポート - Bootstrap CDN の CSP 使用
CSS フレームワークのための Bootstrap をサポート - HubSpot 向けの CSP 使用
監視やマーケティング機能に使われる多機能な Hubspot をサポート - Hotjar 向けの CSP 使用
分析と指標のための Hotjar トラッカーをサポート - WP.com 向けの CSP 使用
wp.com ホスティングをサポート - Akamai mPulse 向けの CSP 使用
オリジンおよびペリメーター連携のための Akamai mPulse をサポート - Cloudflare – Rocket-Loader & Mirage の CSP 使用
パフォーマンス高速化のための Mirage ライブラリをサポート - Cloudflare – CDN.js 向けの CSP 使用
複数のライブラリに対応した Cloudflare のオープン CDN をサポート - jsDelivr 向けの CSP 使用
オープンソース向けの無料 CDN である jsDelivr をサポート
Headers Security Advanced & HSTS WP は、WordPress サイトを保護するために OWASP の CSRF 標準に基づいています。OWASP CSRF 標準を利用し、プラグインをインストールすると、CSRF を完全に軽減するための CSP ルールをカスタマイズできます。他に脆弱なプラグインが存在していても、サイトは安全に保たれます(CSRF)。
Integration with Sentry, Report URI, URIports and Datadog
Sentry is a well-known platform for monitoring and tracking errors in applications. By integrating Sentry with our plugin, users can:
* Receive detailed reports on content security policy (CSP) violations.
* Monitor and analyze JavaScript exceptions occurring on their site.
* Benefit from advanced tools for proactive troubleshooting.
最適なセキュリティのための、Sentry、Datadog、URI Reports との監視・連携。
永久に無料
このプラグインが現在提供しているすべてのセキュリティヘッダー、すべての設定オプション、すべての保護機能は、今後も完全に無料のままです。有料機能の背後に移動する機能は一切ありません。Shield はその上に構築された、まったく新しい別個の監視ツール群です。Shield があることで無料プラグインはより良くなるのであり、悪くなることはありません。
FLoC はまだかなり新しく、まだ広くサポートされていませんが、プログラマーとしてプライバシー保護要素が重要であると考えているため、FLoC をオプトアウトする機能を提供することにしました ! 特別な 「FLoC の自動ブロック」 機能を作成し、常に プライバシー保護とサイバーセキュリティを備えた最高のツールを提供することを主なターゲットとフォーカスとして試みています。
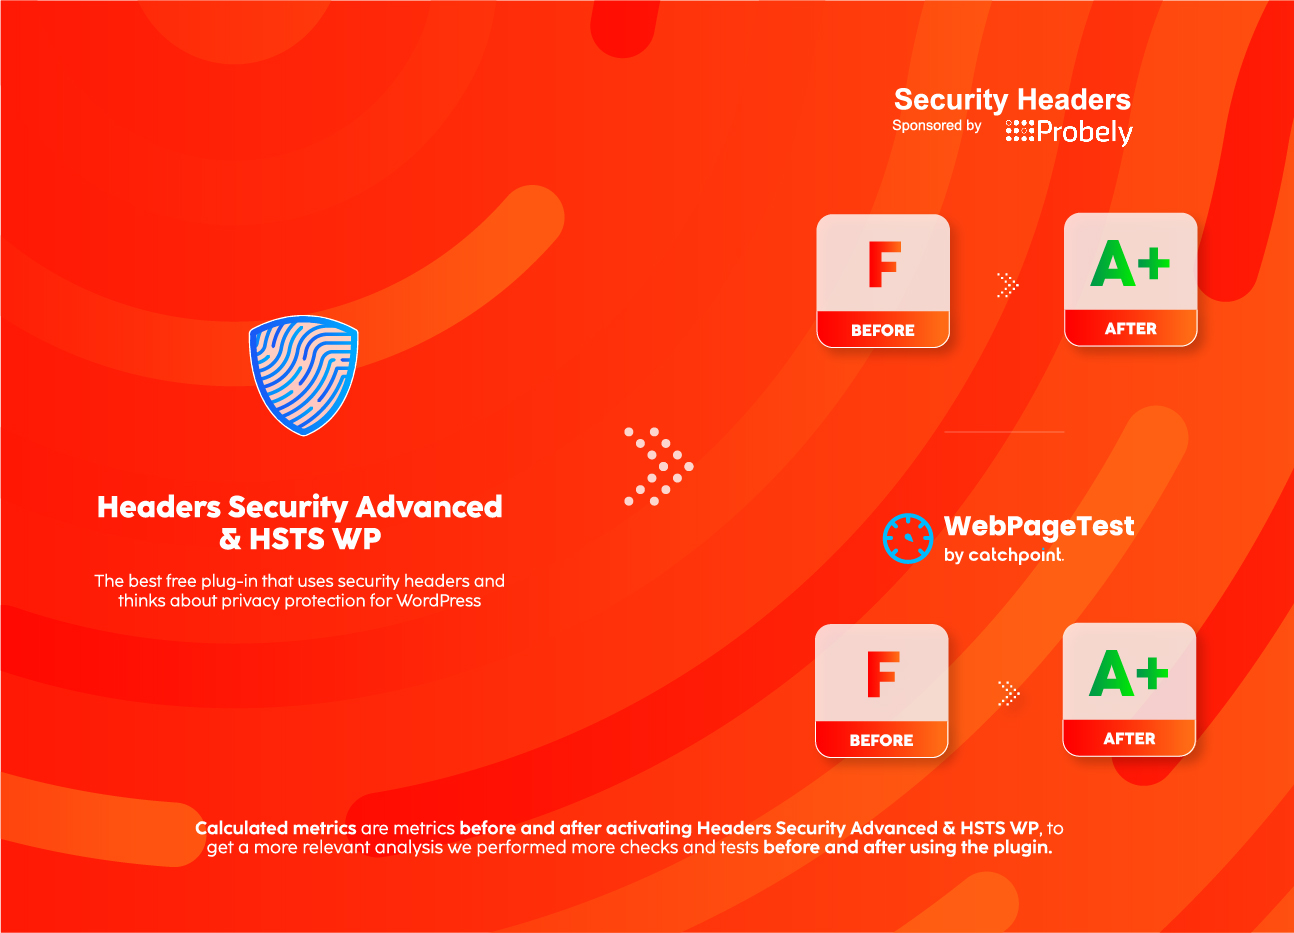
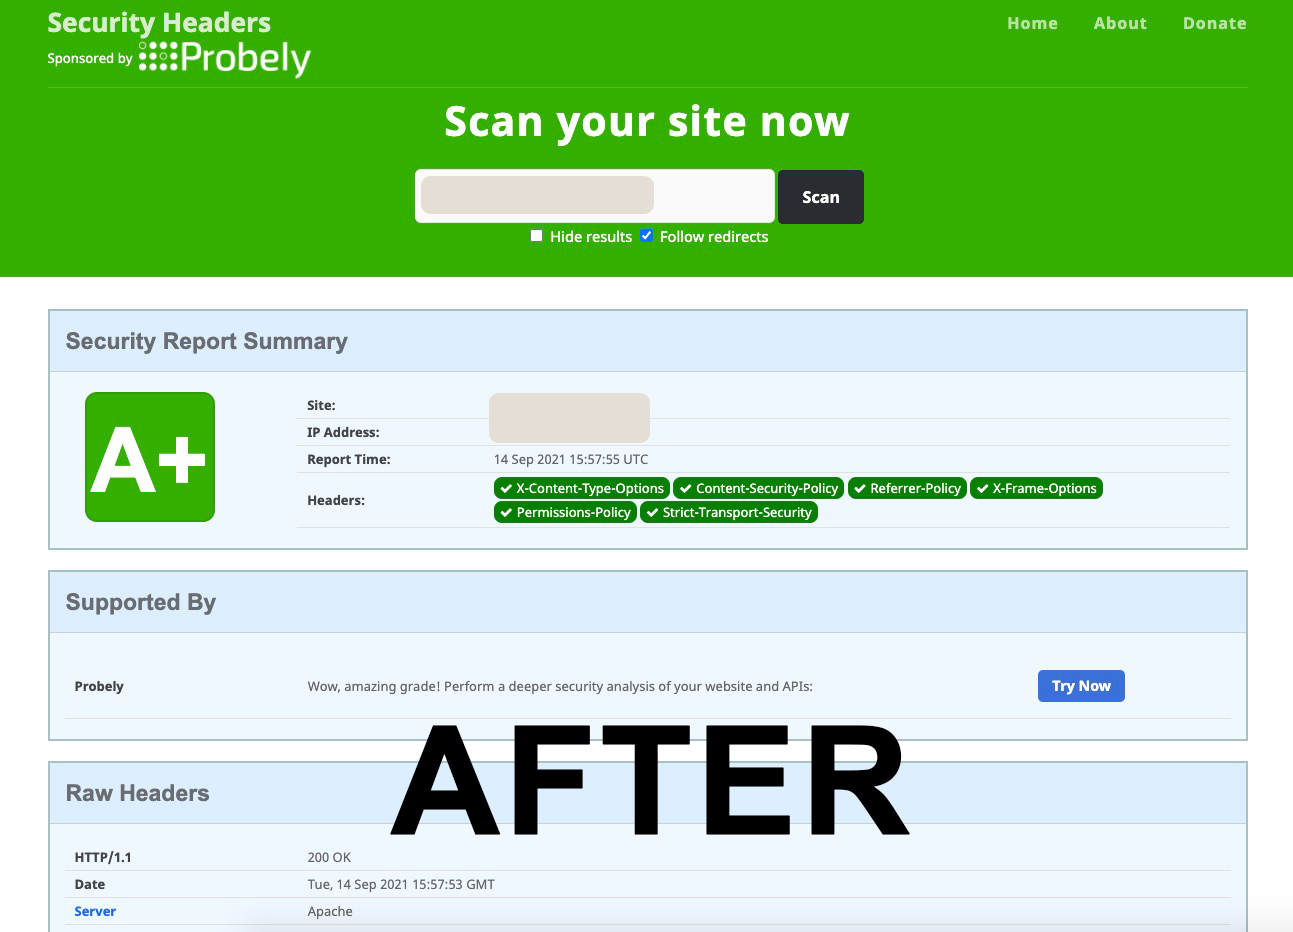
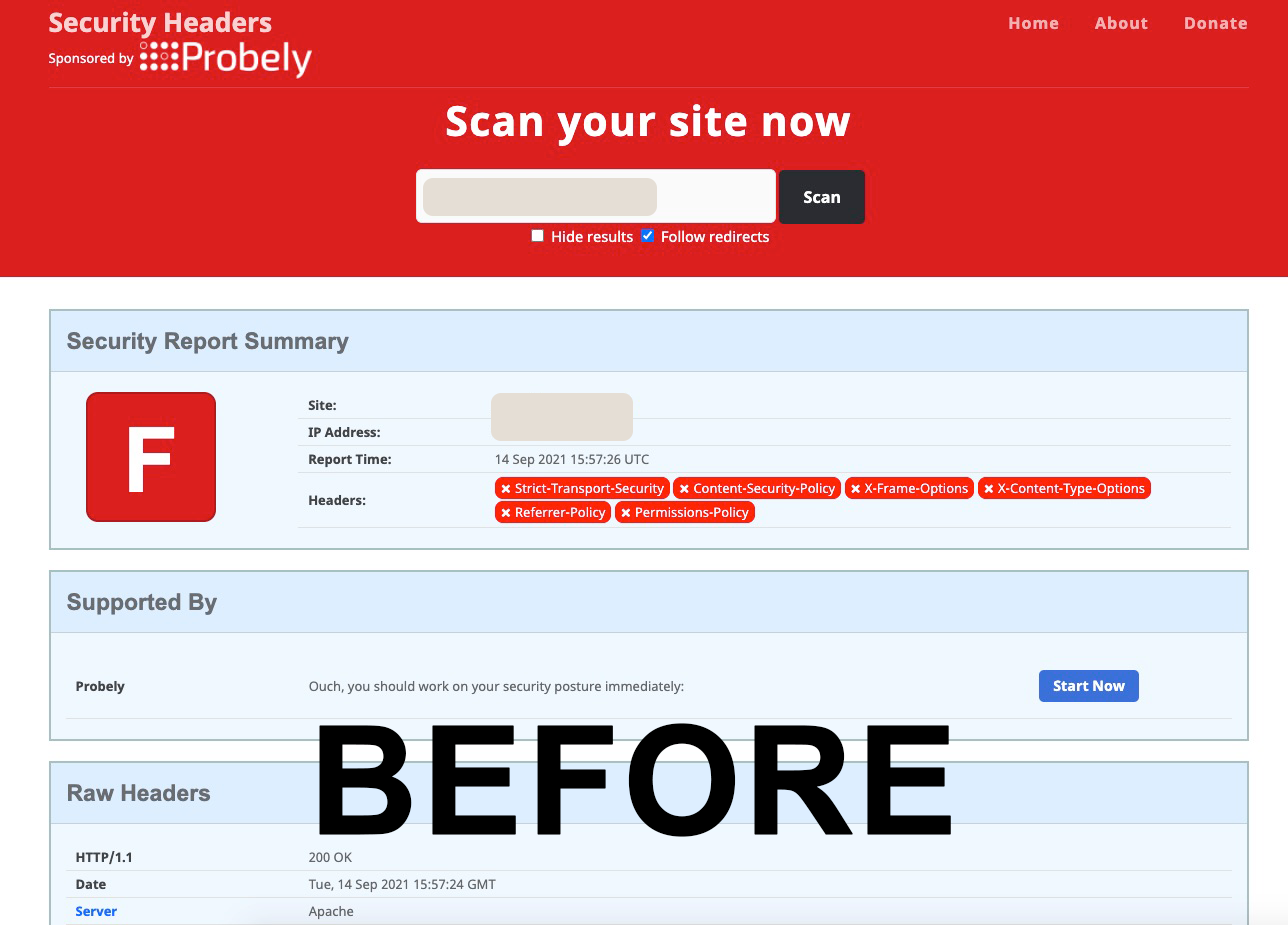
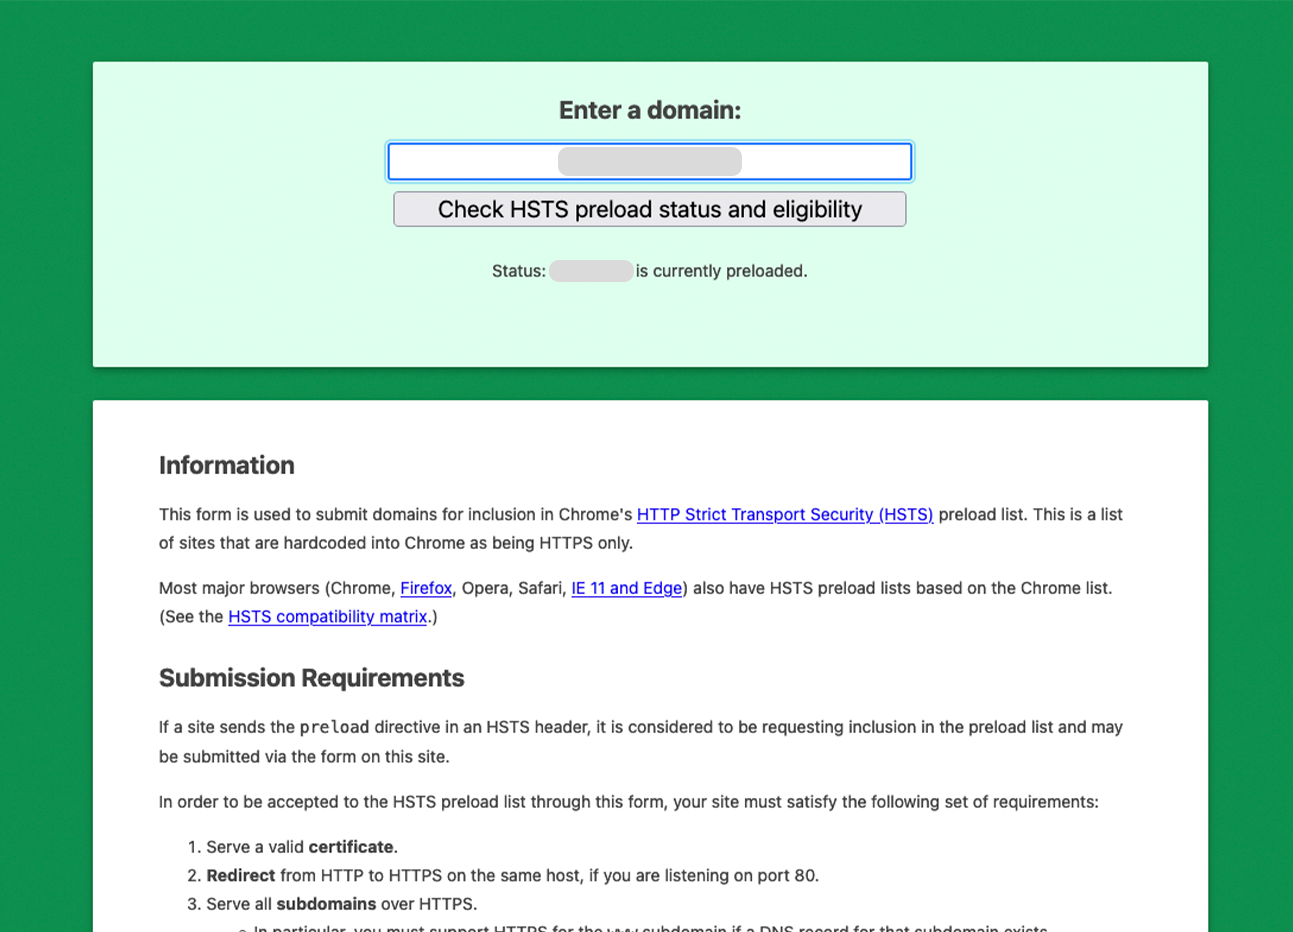
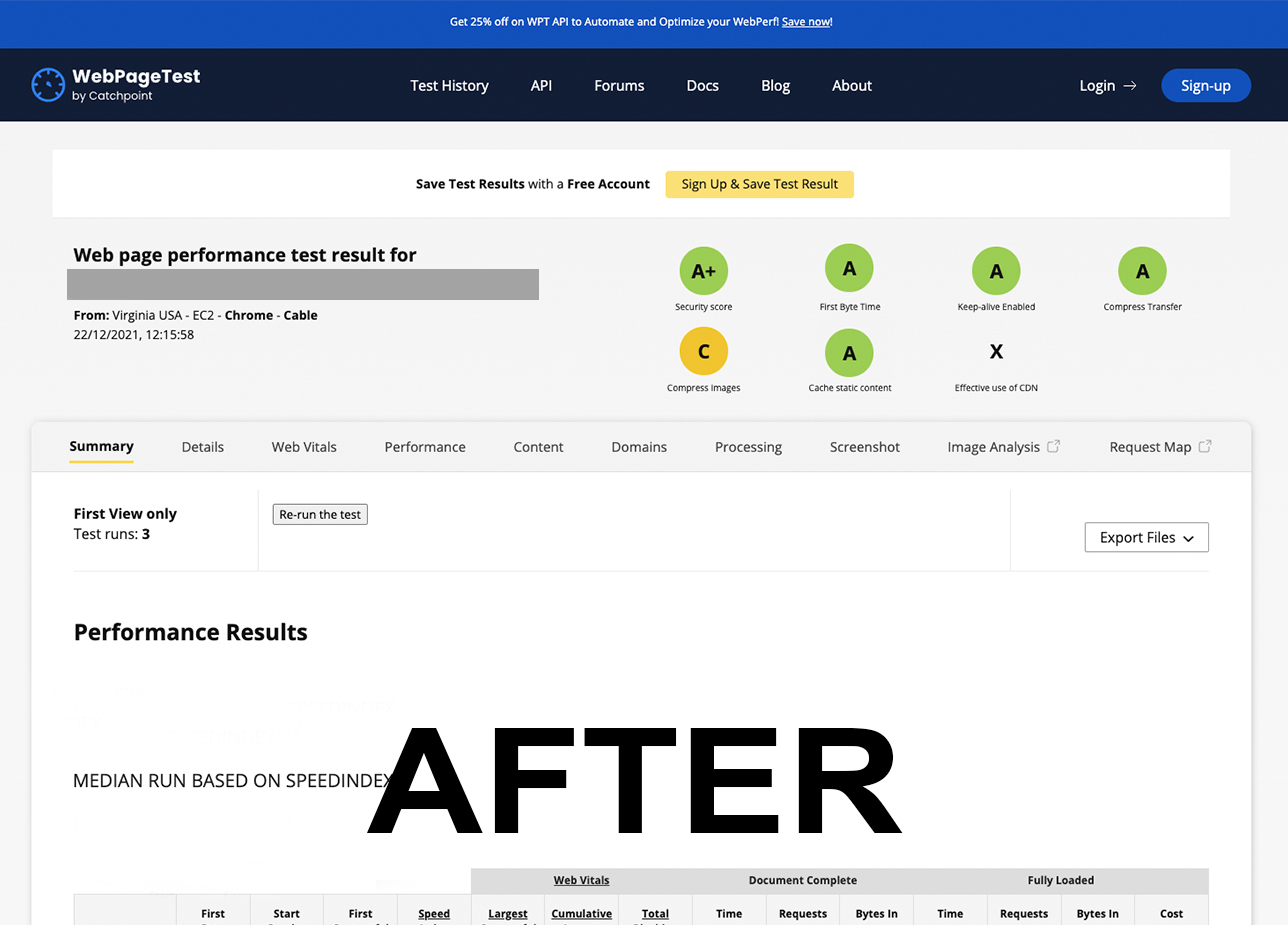
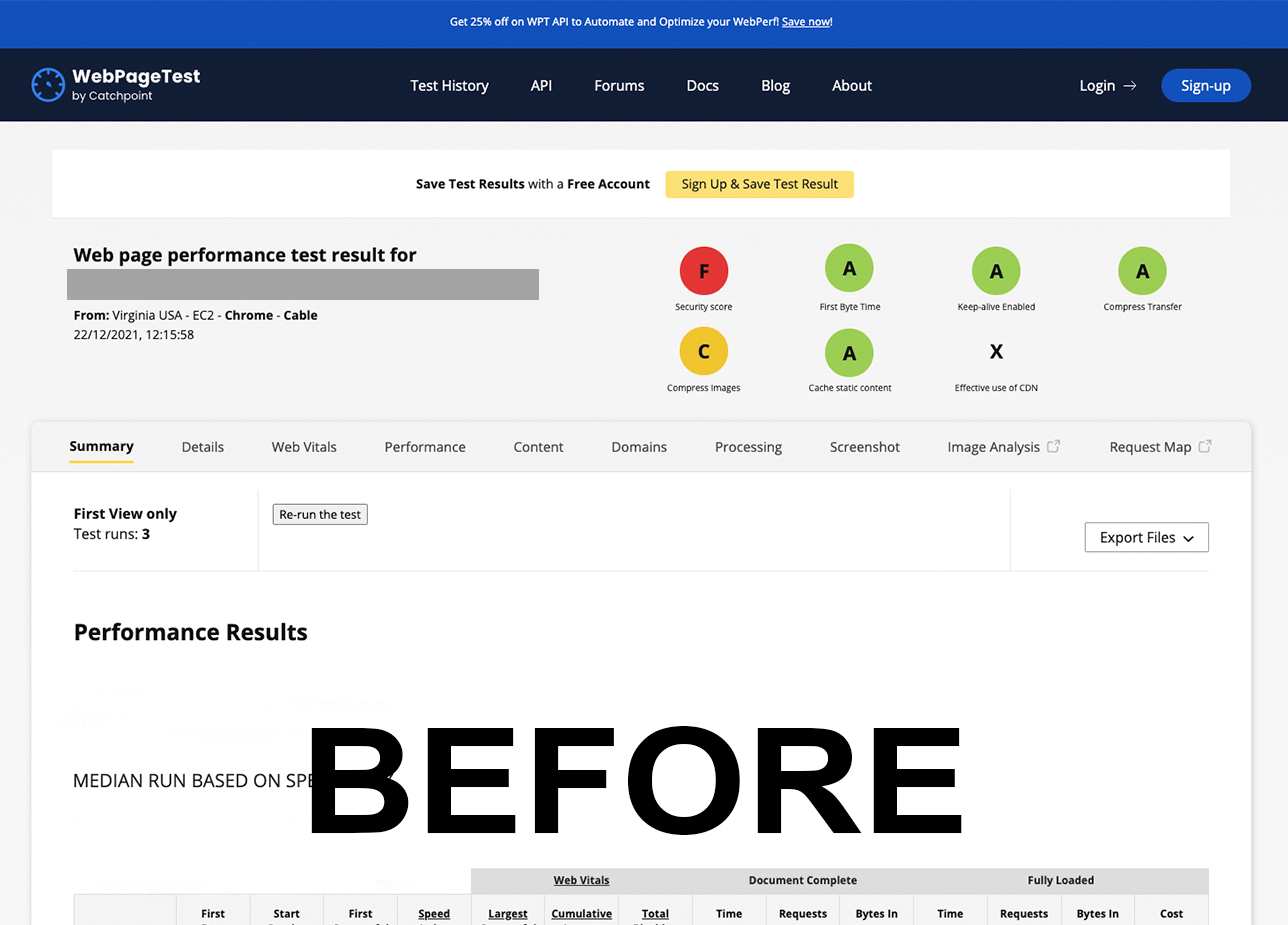
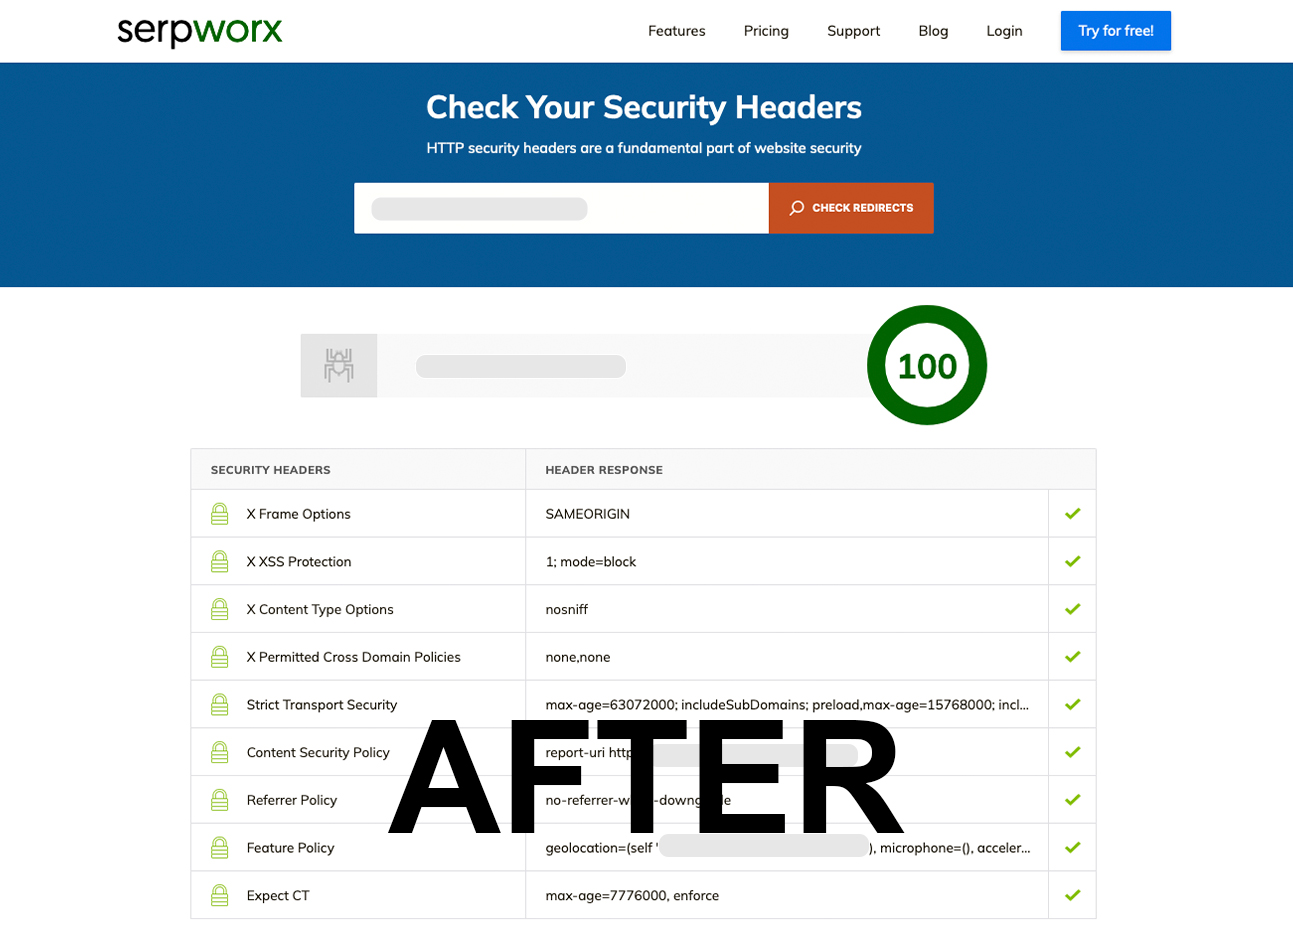
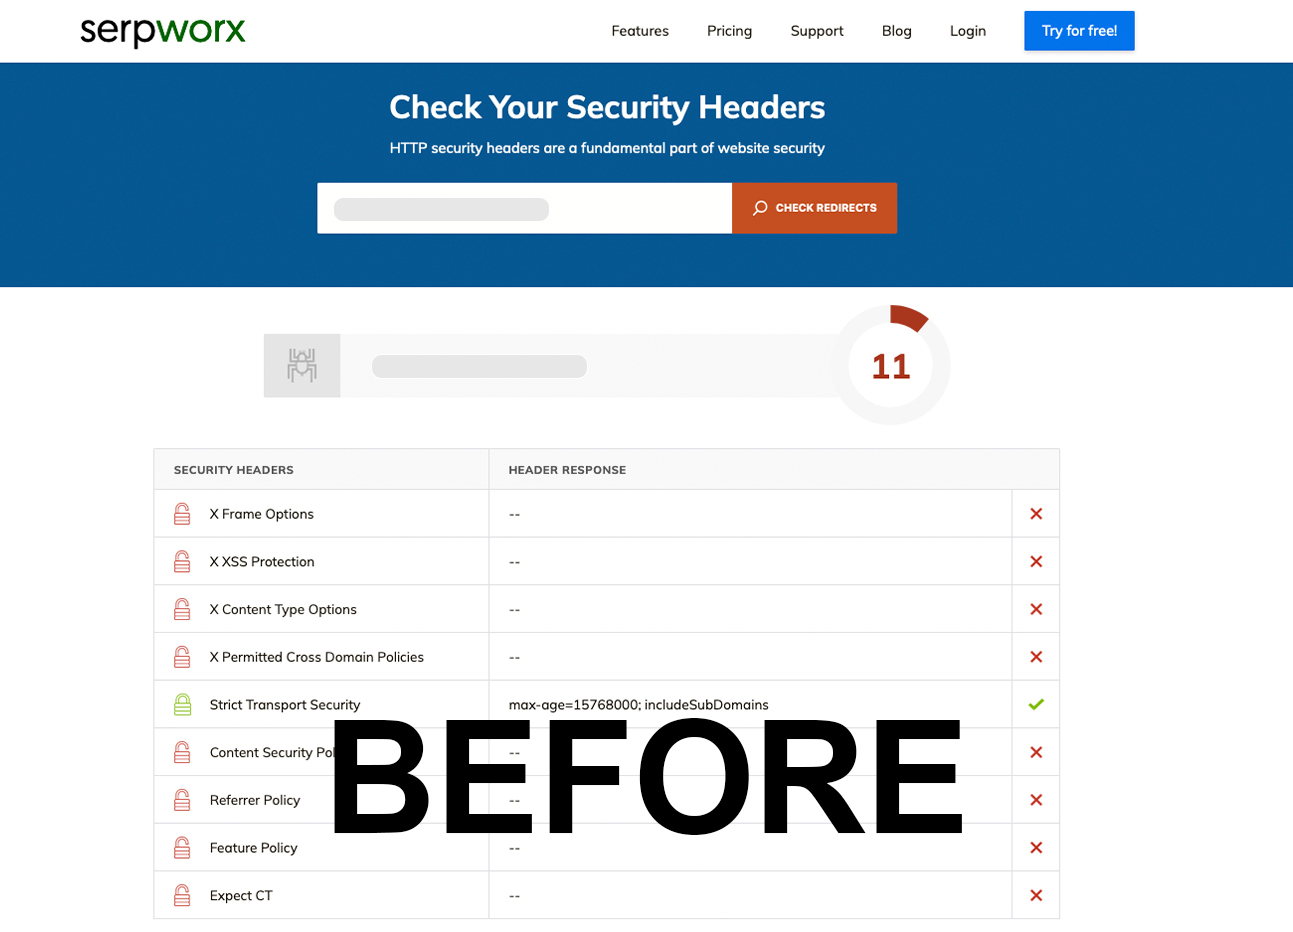
Headers Security Advanced & HSTS WPを使用する前後にサイトを分析します。セキュリティヘッダーは、HTTP セキュリティヘッダーおよび HTTP Strict Transport Security / HSTS のベストプラクティスに従って自己構成されます。
- securityheaders.com で HTTP セキュリティヘッダーを確認
- hstspreload.org で HTTP Strict Transport Security / HSTS を確認
- webpagetest.org で WebPageTest を実行してください
- Web サイトの HSTS テスト gf.dev/hsts-test を確認してください
- CSP テストサイト csper.io/evaluator を確認
- CSP Evaluator csp-evaluator.withgoogle.com を確認
- CSP コンテンツセキュリティポリシージェネレーター addons.mozilla.org
このプラグインは定期的に更新されます。限定的なサポートは無料です。フィードバックをお寄せください (バグ、互換性の問題、または次の更新に関する推奨事項)。私たちはいつでも迅速です:-D.
Shield — 高度な機能(オプション)
このプラグインが現在提供しているすべての機能は、今後も永久に完全無料です。Shield は、より高度な監視や自動化を必要とするプロフェッショナル向けの、まったく新しい別個の高度なツール群です。
- Security Advisor — 設定を分析し、わかりやすい言葉でパーソナライズされた推奨事項を提示
- CSP Guide — おすすめのツール、安全なワークフロー、WordPress 向け CSP スニペット、CSP に関する FAQ
- Security Score Dashboard — リアルタイムの A+ から F までの評価と、10個すべてのセキュリティヘッダーの状態表示
- Email & Webhook Alerts — 変更があった際に、メール、Slack、Discord、Microsoft Teams、またはカスタム Webhook で通知を受け取る
- CSP Violation Analytics — ブラウザがブロックしているリソースとその理由を確認
- Weekly Automated Scans — スキャン履歴と傾向の追跡による自動セキュリティ監査
既存の機能が有料化されることはありません。Shield からの収益は、10万人以上のすべてのユーザーに向けた無料アップデートとメンテナンスの資金に直接充てられます。詳しくは openheaders.org/pro をご覧ください。
Known limitations
- Automatic duplicate resolution needs a self-check that reaches your site’s PHP over a loopback connection. On some reverse-proxy stacks – notably nginx in front of Apache, which is the default on Plesk and cPanel – the backend selects the virtual host by TLS SNI, so a loopback request answers 421 (Misdirected Request) and the self-check cannot arm. When this happens the plugin does not de-duplicate automatically; it keeps sending every header via PHP (nothing is lost), and the Delivery diagnostics panel says so. If a header ends up duplicated on such a stack, set it to “Server only” under “Advanced: per-header delivery” – that keeps the server’s copy and drops the plugin’s own. A future release will make the loopback self-check pin the request to the backend so it can arm automatically on these stacks too.
- Content-Security-Policy is always sent via PHP on the front-end only and is never written to .htaccess, so a strict or nonce-based CSP cannot reach wp-admin or be frozen into a cached response.
- On Nginx and IIS the plugin does not write .htaccess (those servers do not read it). Normal pages are covered via PHP; a server-level cache that serves HTML without invoking PHP needs the equivalent headers added to the server or CDN config. WP Rocket’s cache is served by an early advanced-cache.php drop-in that runs before plugins load; we have modelled this but not verified coverage on a live WP Rocket site, so check its cached responses and add a server or CDN rule if a header is missing.
スクリーンショット
インストール
ITALIAN
- 「プラグイン」の「新規追加」に移動します。
- 「Headers Security Advanced & HSTS WP」を検索します。
- このプラグインを検索し、ダウンロードして有効化します。
- 「設定」>「Headers Security Advanced & HSTS WP」に移動し、ヘッダーをカスタマイズします。
- このオプションはいつでも変更できます。Headers Security Advanced & HSTS WP は自動的に設定されます。
英語
- 「プラグイン」の「新規追加」に移動します。
- 「Headers Security Advanced & HSTS WP」を検索します。
- このプラグインを検索し、ダウンロードして有効化します。
- 「設定」>「Headers Security Advanced & HSTS WP」に移動し、ヘッダーをカスタマイズします。
- このオプションはいつでも変更できます。Headers Security Advanced & HSTS WP は自動的に設定されます。
FRANÇAIS
- 「プラグイン」の「新規追加」に移動します。
- 「Headers Security Advanced & HSTS WP」を検索します。
- Recherchez ce plugin, téléchargez-le et activez-le.
- 「設定」>「Headers Security Advanced & HSTS WP」に移動し、ヘッダーをカスタマイズします。
- Vous pouvez modifier cette option quand vous le souhaitez, Headers Security Advanced & HSTS WP est réglé automatiquement.
スペイン語
- 「プラグイン」>「新規追加」に移動します。
- 「Headers Security Advanced & HSTS WP」を検索します。
- このプラグインを検索し、ダウンロードして有効化します。
- 「設定」>「Headers Security Advanced & HSTS WP」に移動し、ヘッダーをカスタマイズします。
- このオプションはいつでも変更できます。Headers Security Advanced & HSTS WP は自動的に設定されます。
DEUTSCH
- Gehen Sie zu Plugins ‘Neu hinzufügen’.
- Suchen Sie nach Headers Security Advanced & HSTS WP.
- Suchen Sie nach diesem Plugin, laden Sie es herunter und aktivieren Sie es.
- 「設定」>「Headers Security Advanced & HSTS WP」に移動します。ヘッダーをカスタマイズできます。
- Sie können diese Option jederzeit ändern, Headers Security Advanced & HSTS WP wird automatisch eingestellt.
ポルトガル語
- 「プラグイン」>「新規追加」に移動します。
- 「Headers Security Advanced & HSTS WP」を検索します。
- このプラグインを検索し、ダウンロードして有効化します。
- 「設定」>「Headers Security Advanced & HSTS WP」に移動し、ヘッダーをカスタマイズします。
- このオプションはいつでも変更できます。Headers Security Advanced & HSTS WP は自動的に設定されます。
スウェーデン語
- 「プラグイン」>「新規追加」に移動します。
- 「Headers Security Advanced & HSTS WP」を検索します。
- このプラグインを検索し、ダウンロードして有効化します。
- 「設定」>「Headers Security Advanced & HSTS WP」に移動し、ヘッダーをカスタマイズします。
- このオプションはいつでも変更できます。Headers Security Advanced & HSTS WP は自動的に設定されます。
FAQ
-
このプラグインを使うとサイトが遅くなりますか ?
-
No. Headers add less than 1KB to each response. The plugin uses WordPress native hooks and adds no database queries at page load for visitors.
-
Nginx や LiteSpeed でも動作しますか ?
-
Yes. On Apache and LiteSpeed the plugin writes the headers to .htaccess so the web server applies them to every response, including cached HTML and static files, and PHP does not emit a duplicate. On Nginx and IIS (which do not read .htaccess) the headers are sent via PHP, so your normal pages are covered; if you run a server-level cache there, add the equivalent rules to the server config (the plugin’s Settings page shows the exact snippet).
-
キャッシュプラグインでも動作しますか ?
-
Yes. On Apache and LiteSpeed the headers are served at the web-server layer (.htaccess), so they are present even on fully cached pages and on static files that never invoke PHP – including caches that serve static HTML through mod_rewrite: W3 Total Cache (including Disk: Enhanced), WP Super Cache (both “Simple” and “Expert”/mod_rewrite modes), Cache Enabler and WP Fastest Cache. On Nginx and IIS those .htaccess rewrite rules are not read, so a server-level cache that serves HTML without PHP needs the equivalent headers added to the server config by your host; pages served through PHP are covered as usual. Note on WP Rocket: it serves its cache through an early advanced-cache.php drop-in that runs before plugins load, so we do not yet claim coverage for its cached responses on any stack – we have modelled this but not verified it on a live WP Rocket site. If you use WP Rocket, check the cached responses with your browser’s network tab and, if a header is missing, add the equivalent rule at the server or CDN level.
-
Cloudflare でも動作しますか ?
-
Yes. Cloudflare passes through headers set by WordPress. If you also set the same headers in the Cloudflare dashboard, open Settings “Advanced: per-header delivery” and set the matching header to “Off” to avoid duplicates.
-
SecurityHeaders.com で A+ 評価を得るにはどうすればよいですか ?
-
Your site needs all 6 scored headers present: Content-Security-Policy, Strict-Transport-Security, X-Content-Type-Options, X-Frame-Options, Referrer-Policy, and Permissions-Policy. The plugin configures all of these automatically.
-
他のセキュリティプラグインと競合することはありますか ?
-
Rarely. The plugin detects and resolves its own duplicates automatically. If another plugin or your server sets the same header and a duplicate remains, open Settings “Advanced: per-header delivery” and set that header to “Server only” (keep the server copy, drop the plugin copy) or “Off”.
-
HSTS とは何ですか ?
-
HTTP Strict Transport Security は、ブラウザに対して常に HTTPS を使用するよう指示します。ユーザーが http:// と入力した場合でも、ブラウザは自動的に https:// にアップグレードします。プロトコルのダウングレード攻撃を防止します。
-
HSTS にはどの max-age を使うべきですか ?
-
Minimum for preload: 31536000 (1 year). Recommended: 63072000 (2 years). Start with 86400 (1 day) to test, then increase.
-
HSTS Preload を有効にすべきですか ?
-
Only if your entire domain (including all subdomains) works over HTTPS. Preload is hardcoded in browsers and difficult to undo. Removal takes months. Test thoroughly first.
-
What is Content Security Policy (CSP)?
-
CSP は、ページ上でどのリソースを読み込めるかをブラウザに指示します。明示的に許可されていないものはすべてブロックされます。XSS 攻撃に対する最も強力な防御手段です。
-
CSP Report URI はどのように設定すればよいですか ?
-
Enter the report URL from your monitoring service (Sentry, Report URI, URIports, or Datadog) into the CSP Report URI field in Settings. The plugin adds the report-uri directive to your CSP header automatically.
-
コンテンツセキュリティポリシー — ベストプラクティス
-
CSP ディレクティブを記述する際は:
- キーワードには常にシングルクォートを使用する: ‘self’、’none’、’unsafe-inline’、’unsafe-eval’
- CSP 構文内でダブルクォートを使用しない
- Avoid smart quotes (curly quotes) — the plugin converts them automatically but standard quotes are recommended
- プラグインが CSP の入力を検証・サニタイズし、.htaccess のエラーを防止する
-
Shield のライセンスが期限切れになるとどうなりますか ?
-
Your site stays fully protected. All headers keep working. You lose Shield features (dashboard, advisor, alerts, analytics) and revert to the free version. Nothing breaks.
-
バグの報告や機能のリクエストはできますか ?
-
バグの報告や新機能のリクエストは、support@openheaders[dot]org までお寄せください
-
Report URI は何を監視してくれますか ?
-
Report URI will monitor content security policy (CSP) violations and provide detailed reports on detected violations.
-
Datadog は何を監視してくれますか ?
-
Datadog will monitor content security policy (CSP) violations and other security and performance metrics of your site.
-
Datadog の API キーはどこで確認できますか ?
-
Datadog の API キーは、Datadog コントロールパネルの「Integrations」内にある「API Keys」セクションで確認できます。プラグインを有効化すると、有効化の前後でテストを実行します: Datadog で CSP レポートを管理する
-
Sentry は何を監視してくれますか ?
-
Sentry will monitor and log content security policy (CSP) violations and other JavaScript exceptions that occur on your site.
-
プラグインで Sentry 連携を設定するにはどうすればよいですか ?
-
- Sentry のダッシュボードにログインします。
- 「Projects」メニュー項目をクリックします。
- 作成したプロジェクトを選択します。
- 歯車アイコンをクリックしてプロジェクト設定を開きます。
- プロジェクト設定で「SDK SETUP」セクションに移動します。
- 「Security Headers」をクリックします。
- 自動生成された「REPORT URI」の URL をコピーし、プラグイン設定の「CSP Report URI」欄に貼り付けます。Sentry の Report URI の例(例:
https://<your_org>.sentry.io/api/<project_id>/security/?sentry_key=<key>)。 - プラグインが Sentry を初期化し、CSP レポートを Sentry に送信します。
-
プラグインで URIports 連携を設定するにはどうすればよいですか ?
-
- Sentry のダッシュボードにログインします。
- 画面右上の「User Icon」をクリックします。
- 「Settings」をクリックします。
- 設定ページの「Monitored Domains」セクションに、監視したいドメインを追加します。
- 「Security Headers」をクリックします。
- 自動生成された「URIports」の URL をコピーし、プラグイン設定の「CSP Report URI」欄に貼り付けます。URIports の Report URI の例(例:
https://account-subdomain.uriports.com/reports)。 - プラグインが URIports を初期化し、CSP レポートを URIports に送信します。
-
なぜ Sentry、URIports、Datadog、Report URI との連携を選んだのですか ?
-
このプラグインとの連携に Sentry、URIports、Datadog、Report URI を選んだのは、これらがセキュリティ監視の分野で高い評価と機能性を持つプラットフォームだからです。それぞれの概要は次のとおりです。
Sentry
Sentry is a well-known platform for monitoring and tracking errors and exceptions in applications. It provides comprehensive tools for logging and analyzing JavaScript errors, making it an excellent choice for monitoring Content Security Policy (CSP) violations. By integrating with Sentry, users can benefit from detailed error reports and proactive issue resolution.
Datadog
Datadog はインフラ、アプリケーション、ログを監視するための強力なプラットフォームです。CSP 違反を含む、セキュリティおよびパフォーマンス指標を追跡するための豊富な機能を備えています。Datadog と連携することで、ウェブサイトの健全性とセキュリティに関するインサイトを得られ、安全でパフォーマンスの高い環境を維持するために不可欠な、リアルタイムの監視・アラート機能を利用できます。
Report URI
Report URI は、CSP、HPKP、その他のセキュリティヘッダーを含む、セキュリティ違反レポートを収集・分析するための専用サービスです。大量のセキュリティレポートを処理し、詳細な分析と可視化を提供するために特化して設計されています。Report URI を使うことで、CSP 違反を簡単に監視・分析でき、潜在的なセキュリティ上の脅威を迅速に特定して軽減できます。
これらのプラットフォームはそれぞれ独自の強みと機能を備えており、包括的なセキュリティ監視とレポートに最適な選択肢となっています。これらの実績あるサービスと連携することで、WordPress サイトのセキュリティを強化するための、信頼性が高く効果的なツールをユーザーに提供することを目指しています。
URIports
URIports is a well-known platform for monitoring and tracking errors and exceptions in applications. It provides comprehensive tools for logging and analyzing JavaScript errors, making it an excellent choice for monitoring Content Security Policy (CSP) violations. By integrating with URIports, users can benefit from detailed error reports and proactive issue resolution.
-
CSP レポートを Sentry で直接確認できますか ?
-
はい。すべての CSP レポートは Sentry に送信され、Sentry のコントロールパネルで確認・分析できます。
-
どうすれば A+ グレードを取得できますか ?
-
A+ グレードを獲得するには、サイトがすべての HTTP レスポンスヘッダーを発行し、チェックする必要があります。これは、訪問者のセキュリティを向上させるための高いレベルの取り組みを示しています。
-
おすすめのヘッダーは ?
-
HTTP 接続を介して、Content-Security-Policy、X-Content-Type-Options、X-Frame-Options、および X-XSS-Protection を取得します。HTTPS 接続を介して、Strict-Transport-Security と Public-Key-Pins の2つの追加ヘッダーの存在がチェックされます。
- プラグインが有効化されると、テストが実行されます (前後): https://securityheaders.com/
-
プラグインによって速度が低下することはありますか ?
-
いいえ、Headers Security Advanced & HSTS WP は高速で安全で、SEO や Web サイトの速度には影響しません。
-
コンテンツセキュリティポリシー(CSP) — ベストプラクティス
-
プラグイン設定で CSP ディレクティブを記述する際は、無効な設定を避けるために次のルールに従ってください:
1. CSP キーワードには必ずシングルクォート
'を使用するCSP キーワードには、必ずストレートな ASCII シングルクォートを使用する必要があります:
- ‘self’
- ‘none’
- ‘unsafe-inline’
- ‘unsafe-eval’
- ‘strict-dynamic’
これらは CSP 仕様で必須とされています。
2. CSP 内でダブルクォート
"を使用しないダブルクォートはポリシーの外側でのみ使用されます(例: Apache がヘッダーを設定する際など)。CSP 構文の内側では使用しません。
ポリシー内でダブルクォートを使用すると、.htaccess の設定が壊れる可能性があります。3. Do not use “smart quotes” or curly quotes (‘ ’ “ ”)
スマートクォートは、Word、Google Docs、PDF、メールクライアント、モバイルキーボードなどからテキストをコピーした際によく発生します。これらの文字は CSP では無効であり、ブラウザがポリシーを拒否したり、Apache が HTTP 500エラーを返したりする原因になることがあります。
プラグインはスマートクォートを標準的な引用符に自動的に変換しますが、ポリシーを記述する際にはこれらの使用を避けることを推奨します。
5. 無効な CSP を入力した場合はどうなりますか ?
バージョン5.2.4以降、プラグインは自動的に次を行います:
– 丸みを帯びた引用符を ASCII 引用符に正規化する
– CSP 内の無効なダブルクォートを置き換える
– 不正な形式の CSP 構文が .htaccess を壊すのを防ぐ
– 入力が明らかに無効な場合は、組み込みのデフォルト CSP にフォールバックするこれにより、誤った CSP が入力された場合でも、サイトがクラッシュしないことが保証されます。
-
HSTS (Strict Transport Security) とは何ですか ?
-
これは、サイトが HTTPS で実行されている場合にブラウザに安全な接続を強制的に使用させるソリューションとして作成されました。 Web サーバーに追加され、Strict-Transport-Security として応答ヘッダーに反映されるセキュリティヘッダーです。 HSTS は、次の異常に対処するため必要です。
-
Preload HSTSの使用前後のチェック
-
このステップは、ウェブサイトやドメインを承認済みの HSTS リストに送信するために重要です。このリストは Google が公式にまとめたもので、Chrome、Firefox、Opera、Safari、IE11、Edge で使用されています。サイトを公式の HSTS プリロードディレクトリに転送できます。 (‘https://hstspreload.org/’)
-
どのように HTTP Strict Transport Security (HSTS) を使用しますか
-
サイトで Preload HSTS を使用する場合は、アクティブ化する前にいくつかの要件があります。
- 有効な SSL 証明書を取得します。とにかくこれなしでは何もできません。
- すべての HTTP トラフィックを HTTPS にリダイレクトする必要があります (永続的な301リダイレクトを使用することをお勧めします)。これは、サイトを HTTPS のみにする必要があることを意味します。
- HTTPS ですべてのサブドメインも提供する必要があります。サブドメインがある場合は、SSL 証明書が必要になります。
ベースドメイン (例: example.com) の HSTS ヘッダーは既に構成されているため、プラグインを有効にするだけで済みます。
サイトの HSTS ステータスを確認したい場合は、ここで確認できます: https://hstspreload.org/
-
Google の広告技術である FLoC を無効にします
-
FLoC は、すべてのサイトでのユーザーアクティビティを監視し、その情報をブラウザーに保存し、機械学習を使用してユーザーを同様の関心を持つコホートに配置するメガトラッカーです。 このようにして、広告主は同様の関心を持つ人々のグループをターゲットにすることができます。さらに、Google 独自のテストによると、FLoC は Cookie よりも少なくとも95% 多いコンバージョンを達成しています。
-
FLoC by Google を無効にしているのはどうしてですか ?
-
Scott Helme は、5月3日の時点で、最初の100万のドメインのうち967が Permissions-Policy ヘッダーで FLoC の interest-cohort を無効にしていると報告しました。そのリストには、The Guardian や IKEA などのいくつかの大きなサイトが含まれていました。
-
CloudFlare と Headers Security Advanced & を使用できますか ? HSTS WP プラグイン ?
-
プラグインの更新後に異常が発生していますか ? はいの場合は、次の手順に従ってください : CloudFlare クライアントエリアのキャッシュを直接クリアします。
- Cloudflare ダッシュボードにログインし、アカウントとドメインを選択します。
- キャッシュ > 構成を選択します。
- 「キャッシュパージ」 で、「カスタムパージ」 を選択します。 カスタムパージウィンドウが表示されます。
- 「パージ方法」 で、「URL」 を選択します。
- 例に示されている形式を使用して、テキストフィールドに適切な値を入力します。
- 追加の指示に従ってフォームに記入します。
- 入力したデータを確認します。
- クリックして削除します。
これは、cloudFlare が原因です。
評価


貢献者と開発者
Headers Security Advanced & HSTS WP はオープンソースソフトウェアです。以下の人々がこのプラグインに貢献しています。
貢献者

変更履歴
5.3.5
This release brings back server-level header coverage (cached pages and static files) that 5.3.4 lost, without reintroducing duplicate headers.
- Fixed: On full-page caches and static files (CSS, JS, images) the security headers were missing after 5.3.4, because headers were emitted only through PHP and those responses never run PHP. External scanners could report the headers as gone. The plugin now writes the headers to .htaccess again on Apache and LiteSpeed, so the web server applies them to every response.
- Added: Automatic de-duplication is available but is turned off by default in this version. The plugin writes the header to .htaccess and PHP keeps sending it too. On Apache the .htaccess directive replaces, so you still get a single copy. On LiteSpeed .htaccess appends instead, so if a header shows up twice, set that header to “Server only” under “Advanced: per-header delivery” to keep the server’s copy and drop the plugin’s. When automatic de-duplication is enabled, the plugin confirms – by measuring its own live responses – that the server is already sending a header before it stops sending its own copy; if that proof is missing, stale, or uncertain it keeps sending. It always errs toward sending, never toward a missing header.
- Added: A “Run check now” button on the settings page (Delivery diagnostics) shows which web server was detected, whether the .htaccess block is in place, the backend port the plugin learned (or that it has not learned one yet), the exact loopback candidates tried and the responding server, so header delivery can be verified at a glance.
- Added: Per-header delivery control under “Advanced: per-header delivery” (collapsed by default). Each header can be left on “On” (the plugin manages it: it writes the header to .htaccess and PHP sends it), set to “Server only” (keep the server’s or another plugin’s copy and drop the plugin’s own), or “Off” (do not send it at all). With automatic de-duplication off by default in this version, this selector is the primary way to resolve a duplicate: on LiteSpeed, set the affected header to “Server only”. The diagnostics panel points here when it detects a duplicate it cannot resolve on its own.
- Added: On Nginx and IIS the plugin does not write .htaccess (those servers do not read it) and instead shows the exact server-config snippet to hand to your host for server-level caches. Normal pages remain covered via PHP.
- Safety: Every .htaccess write is verified over HTTP and automatically rolled back to the previous file if the site returns an error, and the block is wrapped so a server without mod_headers simply ignores it. The block uses stable markers so upgrades replace it in place instead of stacking, and it is removed on deactivation and uninstall.
- Changed: Any header you had previously disabled is preserved as “Off” under the new per-header delivery control, so no header you intentionally turned off comes back.
- Note: Content-Security-Policy continues to be sent via PHP on the front-end only (never written to .htaccess), so a strict or nonce-based policy cannot reach wp-admin or be frozen into a cached file.
5.3.4
This release fixes duplicate security headers and makes header delivery predictable on every server.
- Fixed: Duplicate headers (Content-Security-Policy, Referrer-Policy, Cross-Origin-*, X-Permitted-Cross-Domain-Policies, Access-Control-Allow-Methods and others) that appeared on Apache and LiteSpeed when both PHP and .htaccess emitted them.
- Changed: Headers are now sent a single time via PHP on all servers. The plugin no longer writes a header block to .htaccess, so there is exactly one source and no duplicates. Any block left by previous versions (including very old formats) is automatically removed on update.
- Fixed: The “disable” checkboxes now work for every header, not just four, and they fully turn a header on or off. The checkboxes have been reset once during the update; a notice explains the change so no site silently loses a header it meant to keep.
- Fixed: The checkbox previously labelled “CSP” actually controlled Permissions-Policy; it has been renamed. Because its meaning changed, it (and the other reset checkboxes) start unchecked. The update notice explains how to re-check any header you want disabled.
- Removed: The deprecated X-Content-Security-Policy header (superseded by Content-Security-Policy).
- Changed: Cross-Origin-Embedder-Policy is no longer sent by default (its previous “unsafe-none” value added no protection and used non-standard syntax).
- Fixed: Removed invalid report-to=’default’ syntax from Cross-Origin headers.
- Fixed: Rewrite rules are no longer flushed during plugin updates or settings saves (fixes multilingual routing breakage with Polylang and similar plugins).
- Changed: The plugin’s Content-Security-Policy is applied to the site front-end; wp-admin is left to WordPress core’s own policy, so a strict CSP cannot break the block editor. All other security headers are still applied everywhere.
- Note: static files (CSS, JS, images) served directly by the web server no longer receive security headers, since headers are now emitted via PHP only. The practical impact is X-Content-Type-Options on static assets. Server-level coverage will return as an explicit opt-in feature in a future release.
5.3.3
このアップデートでは Shield を導入します — より高度なセキュリティ監視を必要とするプロフェッショナル向けの、オプションの高度なツールです。既存のすべての機能は、今後も永久に完全無料です。
- New: Shield tab-based interface (Settings, Dashboard, CSP, Notifications, Export/Import, License, Free vs Shield, FAQ)
- 新機能: パーソナライズされた推奨事項を提示する Security Advisor
- 新機能: Security Score Dashboard(A+ から F までの評価、10個のヘッダー状態の概要表示)
- New: CSP Guide with recommended tools (Csper.io, Google CSP Evaluator, Report URI, URIports)
- 新機能: CSP 違反の分析(ブロック数の多いドメイン、ディレクティブ、傾向)
- 新機能: セキュリティスコアの低下やヘッダーの変更時に届くメールアラート
- 新機能: Webhook 通知(Slack、Discord、Microsoft Teams、カスタム JSON エンドポイント)
- 新機能: 複数サイトを管理する制作会社向けの設定エクスポート/インポート
- 新機能: 履歴を追跡する週次自動スキャン
- 新機能: 検索とカテゴリフィルターに対応した充実の FAQ
- 新機能: 料金体系を明示した無料版と Shield の比較
- 改善: クリーンなアンインストール(ライセンスの自動無効化、すべてのオプションの削除)
5.2.5
何をすべきかを指図するつもりはありませんが、実はこういうことです。Headers Security Advanced & HSTS WP プラグインをアップデートすると、ただボタンをクリックするだけでなく、強化されたセキュリティとパフォーマンスの世界に足を踏み入れることになります。
バージョン5.2.5では、期待以上の体験をお届けするために全力を尽くしました。数多くのバグを解消し、気になっていた表示のズレを改善し、グラフィックをスマートでモダンな見た目に一新しました。その結果は ? 見た目が良くなっただけでなく、さらに使いやすくなったプラグインです。
But that’s not all. This update brings seamless integration with the industry’s leading security monitoring platforms-Sentry, Datadog, and Report URI. These integrations offer enhanced reporting capabilities, providing detailed information on content security policy (CSP) violations and improving site security.
- 更新: WordPress バージョン6.9との互換性向上のためのコード最適化。
- 修正: WordPress 6.9のプラグイン一覧表示との互換性を改善
- 修正: 他のプラグインが
plugin_action_linksフィルターから予期しない値を返した際に、プラグイン一覧の表示が停止することがあるエッジケースを解消 - 強化: サードパーティ製プラグインとの相互運用性を高めるための防御的な型チェックを追加
5.2.5へアップデートすることで、サイトのセキュリティが向上するだけでなく、利用可能な最高のツールで最適化されます。私たちの目標は、最も美しく、最速で、印象的なプラグイン体験を提供することです。それでは、始めましょうか ? 「更新」をクリックして、Headers Security Advanced & HSTS WP とともにセキュリティとパフォーマンスの新時代へ踏み出しましょう。アップデートをお楽しみください !